Data Protection · Cybersecurity · Technology Law
Technology law, informed by the attacker's view.
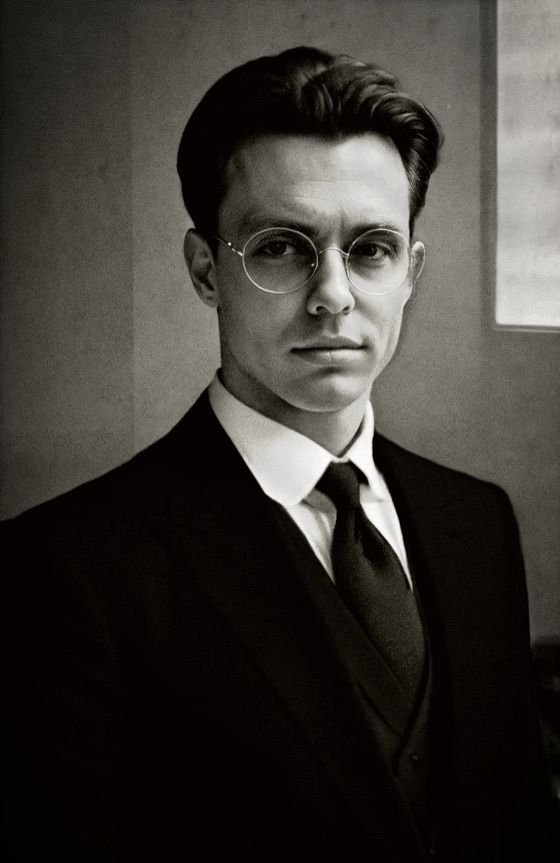
I am Guylian De Wit, a law graduate (LL.M., KU Leuven) with a background in offensive security. I focus on data protection, cybersecurity law and the EU rules that govern digital technology.
- ·Master of Laws, KU Leuven (cum laude)
- ·Advanced LL.M. IP & ICT Law (2026–2027)
- ·Electronics-ICT, Cloud & Cybersecurity (cum laude)
- ·CEH (Practical), 2020
- ·Published CVE (CVSS 7.2)
Profile
I came to law from offensive security. Through Cyber Armed Security, I carried out penetration tests and security audits: I attacked client systems with permission, then explained how to fix what I found. As an independent researcher, I found a zero-day in Centreon's IT monitoring software (CVE‑2019‑19699) and reported vulnerabilities to the University of Cambridge, the U.S. Department of Defense and the IT consultancy delaware.
That work kept raising legal questions. When does a security test become unauthorised access? What may a researcher do with a vulnerability they find, and whom must they tell? Who bears the loss when a known weakness is left unpatched? Those questions took me to KU Leuven, where I earned a Bachelor of Laws and a Master of Laws, cum laude. I am now following the Advanced Master of Intellectual Property and ICT Law.
My research focuses on EU data protection and international data transfers, including a published analysis of the General Court's Latombe judgment on the EU-US Data Privacy Framework. As a trainee lawyer, I hope to work on these questions, on cybersecurity regulation such as NIS2 and the Cyber Resilience Act, and on the IT contracts and disputes around them.
Writing
Publication
Het EU-VS Data Privacy Framework doorstaat eerste juridische toets in Latombe/Commissie
On the General Court's judgment of 3 September 2025 in Latombe v Commission (T-553/23), the first judicial test of the EU-US Data Privacy Framework.
Read article ↗Theses
Protecting the Union's Data: An Analysis of the Applicability of Personal Data Protection Standards to EU Institutional Data
Whether the EUDPR (Regulation 2018/1725) can shield EU institutions' non-personal data held with US cloud providers exposed to the CLOUD Act and FISA 702, arguing it can operate as a de facto protective shield in mixed data sets.
De territoriale gevolgen van het recht op gegevenswissing (“recht op vergetelheid”) volgens artikel 17 AVG (GDPR): Wat is de territoriale reikwijdte van het Europees recht op schrapping van zoekresultaten?
On the territorial reach of the EU right to delisting of search results, and its tension with freedom of expression and access to information.
What are the most common vulnerabilities exploited by malicious actors within an Active Directory environment and how can these be mitigated?
Five commonly exploited Active Directory weaknesses (Kerberos ticket attacks, Group Policy misconfiguration, DCSync, token impersonation and Zerologon): why each exists, and how it is exploited, detected and mitigated. Researched during an internship at EY.
Read (PDF) ↗Education
2026 – 2027 · expected
Advanced Master of Intellectual Property and ICT Law (LL.M.)
KU Leuven, Brussels
Specialisation in ICT, data and intellectual property law at the Centre for IT & IP Law (CiTiP).
2024 – 2026
Master of Laws (LL.M.)
KU Leuven
Major in International & European Law; Minor in Fiscal Law.
2021 – 2025
Academic Bachelor of Laws
KU Leuven
2018 – 2021
Bachelor of Electronics-ICT (Applied Computer Science), Cloud & Cybersecurity
Thomas More Geel
Graduating thesis, researched during an internship at EY, on five commonly exploited weaknesses in Active Directory and how to detect and mitigate them.
Experience
2020 – 2022
Ethical Hacker
Cyber Armed Security · Remote
- Conducted authorised penetration tests, security audits and CIS/ISO compliance assessments for organisations across sectors.
- Assessed cloud (Azure, AWS) and on-premise infrastructure for exploitable weaknesses and advised on remediation.
- Stepped away in 2022 to focus fully on my law studies.
2019 – 2022
Independent Security Researcher
Bug bounty & responsible disclosure · Remote
- Found and reported vulnerabilities through coordinated disclosure, including a zero-day in Centreon (CVE‑2019‑19699). Details under Recognition.
Mar – May 2021
Cybersecurity Consultant (Internship)
EY (Ernst & Young) · Diegem, Belgium
- Researched five commonly exploited Active Directory weaknesses: Kerberos ticket attacks (Kerberoasting, Silver and Golden Tickets), Group Policy misconfiguration, DCSync, token impersonation and Zerologon.
- Reproduced each attack in a lab and set out how to detect and mitigate it, with configuration best practices for Group Policy, in a 141-page bachelor's thesis.
Focus areas
Legal
- GDPR & International Data Transfers
- Cybersecurity Law (NIS2, Cyber Resilience Act)
- IT Contracts & Disputes
- AI Act
- Intellectual Property Law
Technical
- Network, Web Application & Wi-Fi Penetration Testing
- Linux, Windows & Active Directory Security
- Cloud Security Reviews (Azure, AWS)
- Security Auditing & Compliance (CIS, ISO 27001)
- Vulnerability Research & Responsible Disclosure
Recognition
Responsible Disclosure
Centreon
Reported an authenticated remote code execution vulnerability in its IT monitoring software in 2019 (CVE‑2019‑19699); thanked by the Centreon team.
U.S. Department of Defense
Responsibly disclosed a security vulnerability via HackerOne and was recognised under the DoD Vulnerability Disclosure Program.
University of Cambridge
Reported vulnerabilities to the University's CSIRT in 2019; acknowledged and remediated.
“We appreciate you taking the time, and effort, to report this to us responsibly and ethically.”University of Cambridge CSIRT
delaware
Disclosed findings through the company's responsible-disclosure programme in 2019; received a letter of recommendation.
“Thank you for your professional approach for sharing your findings … you are aware of the impact that ethical hacking testing can cause.”Information Security Team, delaware
Published Vulnerabilities
- CVE-2019-19699Authenticated remote code execution in Centreon ≤ 19.10. CVSS 7.2 · High
- CVE-2020-12636Second Centreon vulnerability; reserved, undisclosed at the vendor's request.
Certifications
- Certified Ethical Hacker (Practical), EC-Council, 2020
- CyberOps Associate (Cisco Networking Academy course)
- IBM IT Fundamentals for Cybersecurity Specialization, 2021
- LPI Linux Essentials (LE-1)
- Security Blue Team (Operation Chimera)
Achieved Guru rank on Hack The Box, a hands-on penetration-testing platform; peaked at #2 in Belgium and #151 in the global Hall of Fame. Finalist in the Cyber Security Challenge Belgium (14th in the finals).
Languages
Dutch
Mother tongue
English
Full professional proficiency
French
Professional working proficiency
Russian
Elementary (A1)
Let's talk.
Looking for a traineeship (advocaat-stage) in technology and data law from September 2027.
Letters of recommendation available on request.